21 Dan Saunders ATM Exploit Spree
In 2011, Dan Saunders, a 29-year-old bartender from Australia, discovered a loophole in a National Australia Bank ATM. By repeatedly transferring money between his credit account and savings account during the ATM’s nightly offline window, he tricked the system into letting him withdraw far more than his actual balance. Over the next four and a half months, Saunders spent about $1.6 million on luxury hotels, private jets, and parties before the fraud was uncovered and he was eventually arrested.
22 World of Warcraft’s Corrupted Blood Plague

In September 2005, a glitch in the online game World of Warcraft unleashed the infamous Corrupted Blood incident. A debuff from a raid boss accidentally spread beyond its intended area, infecting players’ characters in major cities and causing a fast-moving digital plague. Healthy players abandoned populated areas, while infected ones were forced into self-imposed quarantines, and the chaos grew so realistic that epidemiologists later studied it as a model for how people might behave during an actual pandemic.
23 GTA Born from Race’n’Chase Glitch
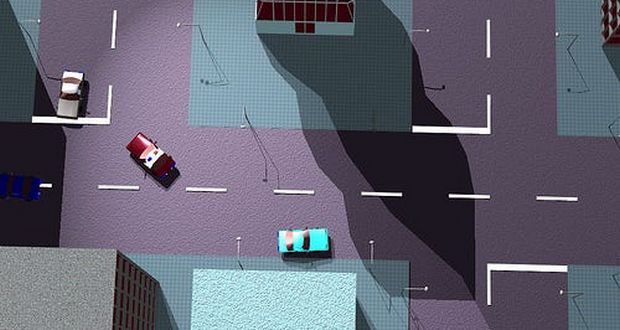
In the mid-1990s, a game developer company named DMA Design (later Rockstar North) was working on a racing game called Race’n’Chase. A glitch in the code caused police cars to behave unpredictably, recklessly ramming into players instead of following standard AI driving rules. Testers loved the chaotic bug so much that the developers rebuilt the entire concept around it, transforming the project into Grand Theft Auto, one of the most successful game franchises in history.
24 Civilization Bug Turns Gandhi Nuclear

In the original Sid Meier’s Civilization (1991), leaders were assigned aggression values on a scale of 1 to 255, with Mahatma Gandhi given the lowest setting of 1 to reflect his pacifism. However, when players adopted democracy, the code subtracted two from every leader’s aggression score, causing Gandhi’s value to drop from 1 to -1. The negative number triggered an integer underflow, wrapping the value around to 255, which was the maximum aggression level, and it turned him into a nuclear-obsessed warmonger in the game despite being in a democracy.
25 John Kane Hacks Video Poker Bug

In 2009, gambler John Kane discovered a flaw in IGT’s Game King video poker machines at casinos in Nevada. By pressing a specific sequence of buttons after a winning hand, he could trick the machine into replaying higher-value hands and collect inflated payouts. Kane and an accomplice earned at least half a million before being caught, but federal prosecutors lost the case after defense lawyers argued, “All these guys did is simply push a sequence of buttons that they were legally entitled to push.”
26 Josh Muszynski’s $23 Quadrillion Charge

In July 2009, Josh Muszynski of New Hampshire bought a pack of cigarettes with his Visa debit card, only to find his account charged $23,148,855,308,184,500, or about 23 quadrillion dollars. The error appeared on his statement along with a $15 overdraft fee, instantly making him the world’s most indebted smoker. Visa later confirmed it was a network processing glitch that briefly affected fewer than 200 transactions before being corrected.
27 Kansas Farm Plagued by IP Mapping Glitch

Since 2002, a farm outside Potwin, Kansas, has been plagued by visits from police, tax investigators, and even lost travelers after being digitally linked to hundreds of millions of devices. A flaw in MaxMind’s IP mapping software placed well over 600 million IP addresses at the farm’s location because the system defaulted uncertain addresses to the geographical center of the United States. For years, the unsuspecting residents endured false accusations and harassment until the company updated its database to fix the error.
Latest FactRepublic Video:
15 Most Controversial & Costly Blunders in History
28 Age of Empires DS Save Bug

In 2006, players of Age of Empires: The Age of Kings on the Nintendo DS discovered a fatal glitch in the game’s save system. If a save file name contained fewer than four characters, the error would corrupt data and permanently brick the cartridge. The developers, unable to patch the flaw, included warning slips in subsequent versions of the game, advising players to steer clear of short file names.
29 United Airlines Revives 9/11 Flight Numbers

In May 2011, United Airlines suffered a computer scheduling glitch that accidentally reinstated flight numbers 93 and 175, both of which had been retired after the September 11, 2001, terrorist attacks. The numbers briefly reappeared in the airline’s booking system, alarming customers who recognized them as the hijacked flights that struck the Twin Towers and were intended for Washington, D.C. United corrected the error and permanently removed the flight numbers after the mistake was reported.
30 Pentium FDIV Bug Costs Intel $475M

In 1994, a flaw in the floating-point unit of Intel’s original Pentium processors led to errors in certain division calculations. For example, dividing 4,195,835 by 3,145,727 produced an incorrect result because of missing entries in the chip’s lookup table. The highly publicized bug forced Intel into a massive recall that cost the company an estimated $475 million.


RE: Fact #37 (Mirai Botnet Downs U.S. Internet for Minecraft) – That guy, Paras Jha, who was a student at Rutgers, got curious about making money with DDoS attacks. He actually did some small-scale attacks on his own university’s systems, timing them with big events like registration and midterms, all while trying to get them to hire him to stop those very attacks. What an amoral little sh*t, wasn’t he.
RE: Fact #30 (Pentium FDIV Bug Costs Intel $475M) – The joke back then was something like, “Why did Intel name it the Pentium instead of the 586? Because they did 486 + 100 and got 585.9996!”
RE: Fact #18 (Patriot Missile Bug Kills 28 Soldiers) – Not preventing something isn’t the same as causing it.
RE: Fact #49 (CIA Sabotages Soviet Pipeline Software) – Seriously, this just goes to show that software piracy can lead to some really major problems.
RE: Fact #20 (Nebraska Woman Exploits Gas Pump Glitch) – I remember when this was a new story. It was about her giving other people free gas, right?
My oldest kid totally cracked the code: “talk less, get more.” Basically, if they want an exception or something extra, they’ve learned not to rub it in their siblings’ faces. The other kids are starting to catch on too. It really pays off to know when to keep quiet and not push your luck.
As they say, some people get by and others get taken down.
This reminded me of when the campus vending machine gave me dollar coins instead of quarters. I didn’t tell anyone, I just kept playing that coin return lever like a slot machine and left feeling a little less broke as a college student.
RE: Fact #35 (Slammer Worm Overwhelms Internet in Minutes) – I was on the night shift in our SOC, and I actually got to see it all go down live! Hundreds of sensors across tons of customers started flashing red all at once. Definitely a night I won’t forget.
That’s really cool you’re an SOC veteran! As an SOC chief myself, it’s rare to meet folks who were on the SOC/RRT beat that long ago. Did you see any other big historical moments back then, like the I Love You worm or any zero-day exploits?
I remember the Max Headroom takeover. I thought that was so badass when I was a kid.
RE: Fact #15 (Bungie Recalls Myth II Uninstaller Bug) – They’ve had a few hiccups with releases before. For example, Halo 2 on PC got pushed back because a picture of a developer’s backside was found buried in the game’s files. And even though it wasn’t directly Bungie’s fault, Halo Infinite was delayed for a whole year, supposedly due to COVID, but I suspect they just needed more time to get it right.
RE: Fact #4 (Jimmy Zhong Exploits Silk Road Bug) – Back then, Bitcoin wasn’t worth as much, so it wasn’t a huge amount when he took it. I also think he helped Silk Road fix the glitch later on. Apparently, he said Ross Ulbricht told him he could keep it as a reward for his help.
Sounds like Ross might have sent him more bitcoins to help fix it.
RE: Fact #8 (USS Yorktown Crashes from Zero Division) – Seriously? It took them 2 hours and 45 minutes just to turn it off and on again? Sounds like someone couldn’t remember the username and password!
RE: Fact #48 (Michael Collins Fixes Apollo 11 with Switch) – So, plot twist: that was actually the *only* step in Procedure 17.
RE: Fact #9 (UK Post Office Horizon Scandal) – The Post Office and Fujitsu were aware of this issue and deliberately hid it for over a decade. Postmasters lost everything – their homes, families, marriages, friendships, and even their lives because of it. It was only thanks to the persistent reporting by Private Eye that it stayed in the public consciousness.
RE: Fact #35 (Slammer Worm Overwhelms Internet in Minutes) – Slammer lives only in the computer’s memory and never saves itself to a disk. It doesn’t change anything on the system, so getting rid of it is as simple as turning the computer off.
That’s awesome! It’s kind of like a real virus – super easy to catch, but hopefully just as easy to get rid of.
This is one virus where nobody minds if the patient dies, ’cause you can just flip the switch and turn them back on.
RE: Fact #37 (Mirai Botnet Downs U.S. Internet for Minecraft) – They offered DDoS protection for Minecraft servers and then DDoS’d competitor servers to push people towards their services.
RE: Fact #16 (Deep Blue Bug Shakes Kasparov) – Kasparov is pretty sure they had a chess master helping the computer, but they wouldn’t let him see any of the code or go back to the room at all, even before, during, or after the game. He thinks this lack of transparency made him even more suspicious.
Wanna make someone even more convinced they’re right about something? Don’t explain away their fears. That’ll totally help.
It kinda makes sense to show it before and during, but why not show how it worked afterward too?
What kind of proof would sway a programmer who doesn’t work with AI? Just showing them millions of lines of code probably wouldn’t be that effective.
Back then, it was top-notch stuff. Plus, I bet they wanted to show it off to others to prove it was legit. Still a bit strange though.
RE: Fact #6 (San Diego Fireworks Launch Glitch) – I was there for it! For a few seconds, it was absolutely amazing. Then there was this weird, awkward pause as people processed what happened. After that, it was a mix of being amused and a little let down.
Honestly, I wouldn’t have minded at all. I’ve seen a ton of fireworks displays, and you don’t get to see something like that very often.
RE: Fact #13 (Y2K38 Time Overflow Looms Ahead) – For 64-bit systems, the equivalent date should hit in about 290 billion years. Might be a good time to get your IT systems ready now.
That’s the best part of 512-bit systems. They totally skip past the 64-bit fatal error.
What about the 128-bit and 256-bit versions?
What if we just waited until December 2037 and then scrambled to get it done at the last minute? I’m sure that would work out perfectly, right? At least one company somewhere would probably do that.
We could give people Christmas off and have them start back after the holiday, since it’s not until mid-January 2038 anyway.
RE: Fact #21 (Dan Saunders ATM Exploit Spree) – This totally reminds me of a story. Back in the mid-80s, I missed my train to London and ended up stuck all night at Gare Saint-Lazare in Paris. I had just enough cash on me to fly to London the next day, but not enough to get to the airport. The only way I managed to get back was because there was a payphone in the station that actually gave you back double the money you put in for any call you made. Otherwise, I guess I’d probably still be there!
I once bought a soft pretzel with my credit card, and my bank flagged it as rejected just three minutes later. I ended up just leaving without paying for the pretzel and then left the country a few days later. Now I’m just waiting for Interpol to show up at my door with an extradition order.
You totally swiped a soft pretzel on international free soft pretzel day!
Back in the day, we’d find phones like that at the London airport. We’d grab any spare change first, then figured out it’d give more back if you put in too little, dialed a wrong number, and hung up. We used that to buy candy!
RE: Fact #17 (F-16 Simulator Equator Sign Error) – I worked on avionics simulators back in the 1980s. There are tons of stories about simulators and real planes acting weird when they:
Go below zero feet
Go above 32,767 or 65,535 feet
Fly over the equator
Back then, computer graphics were pretty basic, and there were a bunch of issues. The funniest one I recall was a simulator where a plane flew behind a barn. But the HSR module had a glitch, so instead of the plane vanishing, the barn disappeared and the plane was still visible. That last one, at least, was spotted and fixed super fast.
RE: Fact #14 (Panasonic Children’s Game Swears Aloud) – In programming, we sometimes call that a “feature” instead of a “bug”!
In the consumer world, we basically call that, “Why the fu*k did nobody test this program before selling it?”
RE: Fact #4 (Jimmy Zhong Exploits Silk Road Bug) – Lesson one: Don’t call the cops asking about money you stole that’s gone missing.
Especially if it’s just a tiny bit of what you earned. Also, who ratted him out to the feds for stealing money from Silk Road?
Basically, it was a bunch of bad calls, but the main reason he got busted was he messed up and sent money from the wallet they were watching to an exchange that had his actual name. Just one transfer out of loads, but that was all it took.
Lesson 1: instead of stealing $3.4 billion, maybe aim for like $3 million. You’d still live pretty comfortably and wouldn’t be all over everyone’s radar.
He stole it for about 3 million. The billion-dollar valuation happened years later after Bitcoin took off and he was caught.
RE: Fact #21 (Dan Saunders ATM Exploit Spree) – I could never have pulled that off, knowing it would all blow up eventually. Plus, not knowing if he’d get off easy would have stressed me out completely.
So, in the interview, he talks about how he wasn’t actually caught. He just felt really bad about it and confessed to the bank. When they didn’t do anything, he went to the media with his story, and that’s when people finally took it seriously.
So, reading the story, I’m not entirely convinced he wouldn’t have eventually gotten caught. Even when he called the bank, they seemed to imply they knew someone was messing with the money, even if they weren’t sure who it was. Plus, it just feels like there’d be some digital breadcrumbs they’d find eventually, right? It’s wild he managed to keep it going for so long. Turning himself in definitely sealed his fate faster, but I really think he would’ve been caught one way or another.
If I had over a million bucks, I’d totally ditch and move to a new country.
RE: Fact #34 (Welchia Worm Tries to Patch Windows) – Reminds me of that luck virus from Red Dwarf!
RE: Fact #10 (Mazda Bricked by 99% Invisible Bug) – It was also happening to Mazda systems that tuned to a Seattle radio station.
So, it turns out that station, which is an NPR one, accidentally sent their logo without a file extension. This totally messed up the infotainment system, making it get stuck in a loop because it didn’t know how to handle that.
A bit of data validation could’ve prevented both of these problems. But hey, who has time for that when you’re only got a week to get it done, right?
RE: Fact #22 (World of Warcraft’s Corrupted Blood Plague) – The same year, on July 7th, London had a bunch of bombings. The very next day, someone decided to joke about it on my EU game server.
The earliest raiding dungeon, Molten Core, has a boss named Baron Geddon. Geddon can cast an ability that turns a random player fighting him into a living bomb that explodes after a short time, hitting nearby friendly players for a lot of damage.
A high-level hunter went into Molten Core, fought Geddon, and let their pet get the living bomb debuff. Then, they dismissed the pet, which basically hides it away, kind of like a Pokemon.
After heading back to the city, the hunter released their pet right in the middle of the busy Ironforge auction house, killing tons of lower-level players and causing chaos in the general chat.
I thought the Hakkar plague was really funny, and I even did it myself, but the auction house bombing felt like it was a bit too soon.
Back when boss mods were a thing, people would get a bunch of whispers saying “YOU ARE THE BOMB YOU ARE THE BOMB YOU ARE THE BOMB.” We actually made macros to make them think they were the bomb.
RE: Fact #23 (GTA Born from Race’n’Chase Glitch) – It’s pretty wild how this glitch is now a huge part of the racing game experience.
RE: Fact #27 (Kansas Farm Plagued by IP Mapping Glitch) – It’s not a glitch, it’s just how it was designed. IP addresses weren’t really made with the idea of giving out physical locations to random people, but they don’t actively try to hide that info either.
RE: Fact #14 (Panasonic Children’s Game Swears Aloud) – This makes me think of the old Speak and Spell toy. If you turned it on and pressed backspace, it would sometimes go wild and just play a constant stream of random sounds.
Yeah, that was only in the first ’70s model, unfortunately. They fixed that bug when they changed from round buttons to the membrane. I remember getting the new version for Christmas, but one of my neighbors had his older brother’s version, and we had a blast with it randomly spouting stuff.
RE: Fact #2 (Cosmic Rays Flip Memory Bits) – This is seriously the coolest thing I’ve learned today! I’ve been in IT for a decade, and you know how sometimes weird errors would pop up just once or twice and then *poof*, never again? Yeah, this makes sense.
This is a great one to keep in mind for those times when an explanation is obviously needed but not provided. I’ve been calling those ‘when the stars align’ errors until now.
RE: Fact #47 (Therac-25 Radiation Bugs Kill Patients) – Totally, this is a classic case of why you gotta do thorough investigations when a patient gets hurt to figure out exactly what went wrong.
So many error messages just said “MALFUNCTION” with a number. The manual didn’t explain them at all, or even hint that they could be dangerous for patients.
Some things never change in Biomedical Engineering, huh? But hey, just call the manufacturer with your purchase order ready, and they’ll find the info for you. Maybe they’ll send a tech right away, or maybe they’ll just tell you to reboot and call back. Still, if Apple is backing down on the right to repair, there’s hope for us in the Biomed field.
In one of my computer science classes, this was brought up as an example of how some software needs hardware failsafes.
RE: Fact #28 (Age of Empires DS Save Bug) – I was wondering why this game suddenly stopped working! It’s the only DS game I’ve ever had that happened to. I tried all sorts of cleaning solutions on the pins, and even thought I’d somehow dropped and broken it. This fact really surprised me though. I remember enjoying it a lot, it reminded me of Advance Wars, and that’s why I put so much effort into trying to fix it.
Glad this fact gave you closure.
RE: Fact #11 (Boeing 787 Needs 51-Day Reboots) – Yeah, a lot of planes do that. I used to fly one where the screens in the cockpit would just switch off after 24 hours if they weren’t reset. So, we made it a habit to turn them off and back on every morning before we started flying.
You really don’t want those screens to go black while you’re flying, especially if the plane was left powered on overnight. It’s not a huge deal if they do, just takes about 30 seconds to get them back. But it’s definitely not ideal if it happens at a critical moment.
Also, when other weird glitches or error messages pop up with the electronics, maintenance folks often tell us to “go dark” – basically, turn the whole plane off and then back on. So, if you’re ever boarding and the lights and fans suddenly cut out for a bit, that’s probably what’s happening. It’s totally normal, kind of like rebooting your computer. So much of it is computerized and linked together.
And yep, the critical stuff has backups and redundant systems. Plenty of planes have three or more layers of protection. One plane I flew could still fly with three out of four generators down. And if we lost the last one, we’d still have about 30 to 60 minutes of battery power.
So, I had a flight a bit ago where they had to restart the entertainment system like, a bunch of times while we were still on the ground. And get this, every single screen ended up showing the Linux boot log!
Yeah, totally happens all the time. Some planes have a special ground services bus that only handles the entertainment system and the power at your seat. Depending on what the airline says, the flight attendants can even try resetting that themselves without asking. It’s totally separate from the rest of the plane’s important electrical stuff, so no worries about messing anything else up.
As a software engineer, I’m happy but also a little weirded out that “have you tried turning it off and on again?” works for planes too lol.
It happens all the time! Components often need to be certified, which means you can’t just swap them out later. Doing so would involve a ridiculous amount of paperwork and testing. Like, imagine an airplane from the 90s that still used a 3.5″ floppy disk for its avionics database – that’s 25 years later! The thinking seems to be that you never know what changing something might screw up, so it’s best not to touch it.
I’m an avionics tech, and let me tell you, I’ve “fixed” tons of avionics issues just by turning the plane off and back on again.
RE: Fact #34 (Welchia Worm Tries to Patch Windows) – When the tech support person is totally over having to fix all the basic stuff.
If I were fixing everyone’s computers, I could just hang out on Newgrounds all day.
Wow, that phrase sounds like it’s from way back in 2005.
RE: Fact #9 (UK Post Office Horizon Scandal) – It’s estimated that 13 postmasters took their own lives due to the allegations. Even though the Post Office knew the software was buggy, they continued prosecuting people, knowing the software was the problem.
And think about the millions of pounds the Post Office took from sub-postmasters as ‘discrepancies’ – money that wasn’t even theirs to begin with. Now, that money is just gone, and the Post Office can’t afford to pay it back.
The Post Office can totally afford to repay it.
Revenue was £912 million and net income was £22 million some time ago.
Seriously, the Post Office, the government, and the Ministry of Justice are all to blame here. I think the Post Office should be forced to cut costs and sell off some assets to pay back everything they owe, with interest. If that’s still not enough for them to keep running, then the government should cover the rest since they own the Post Office. Plus, they should compensate the victims for all their losses during this mess. And honestly, the folks who messed this up should be prosecuted for fraud and manslaughter or something similar, especially since they apparently knew the software was bad.
Hope they go after the prosecutors who knew it was a software problem.
RE: Fact #1 (Excel Autocorrect Breaks Gene Names) – What’s frustrating is that the auto date correction feature isn’t intuitive and doesn’t line up with how Excel usually works. Like, Excel already warns you if formulas in nearby cells are different, because most people want those to be the same. So, why does pasting a list of text strings into Excel automatically convert some of those nearby cells to dates? It’s just poor design that Microsoft hasn’t corrected.
RE: Fact #14 (Panasonic Children’s Game Swears Aloud) – So, the takeaway here is that writers swear a lot, or maybe that’s the secret to the Secret Writer Society.
As someone once put it, you write when you’re drunk and edit when you’re hungover.
Seriously, don’t try this, it doesn’t actually work.
RE: Fact #19 (Loganair Flight Saved by Autopilot Disconnect) – Saw this on Air Disasters and the whole thing is pretty wild. Apparently, the plane got hit by lightning right on the nose. The pilots probably got blinded and super confused by that. After the strike, they thought the autopilot had turned off and started flying manually, but it actually hadn’t and was still working fine. The SAAB 2000 they were flying is one of those planes where you can’t just override the autopilot. So, when the pilots tried to make it climb, the autopilot kept pushing it down instead. This led to a super fast dive that the pilots couldn’t do anything about. The autopilot finally cut out due to a random computer glitch just 7 seconds before hitting the ground, which is when the pilots got it back and managed to land safely.
RE: Fact #25 (John Kane Hacks Video Poker Bug) – So, Kane would start with a game like Triple Double Bonus Poker, playing at the lowest bet, like $1. He’d keep playing until he hit a big win, say $820 at the Silverton.
Then, he’d switch to a different version, like straight Draw Poker, and play until he won anything at all. The idea was to get the machine to offer a “double-up,” where you bet your winnings on a simple high-card draw. This double-up offer, apparently due to a glitch, was key. If the machine didn’t have this option, it wouldn’t work.
The quote basically says that letting people replay hands would take away the chance aspect and defeat the purpose of gambling, which goes against poker rules.
After that, Kane would add more money or a voucher, then leave the Draw Poker game and change the bet to the maximum, like $10 at the Silverton.
When he went back to Triple Double Bonus Poker, his $820 win would still be there. He could then cash out, and the machine would give him that jackpot again. But here’s the kicker: it would recalculate the win at the new, higher bet, netting him $8,200.
RE: Fact #12 (Azer Koçulu Deletes Left-Pad Package) – Open source drama can range from this to the core.js guy who ran someone over.
Your wording made it sound like an npm package issue led to a pedestrian dying, which honestly wasn’t that surprising to me.
RE: Fact #35 (Slammer Worm Overwhelms Internet in Minutes) – That would have been even worse, but thankfully the flaw in the way it picked IP addresses helped a bit.
RE: Fact #24 (Civilization Bug Turns Gandhi Nuclear) – Even when it goes past zero with subtraction, it’s still called an Integer Overflow. An underflow happens when a computer can’t quite store the answer to a calculation because it’s too small for the type of data it’s using.
Yeah, it makes more sense when you remember computers actually subtract by adding.
That was really interesting. Thanks!
RE: Fact #12 (Azer Koçulu Deletes Left-Pad Package) -His package was called “left-pad” from npm. It was only 11 lines long and just added characters to the beginning of a string.
He did this because he had a disagreement with Kik Messenger about the name “kik” on npm, which he owned. Things got heated, and npm ended up taking the name away from him and giving it to Kik.
Turns out, “left-pad” was used by a bunch of really important JavaScript projects, like Babel, Webpack, React, and React Native. If those names don’t ring a bell, just know that a huge part of the internet and major companies like Meta, PayPal, Netflix, Spotify, and even Kik rely on them.
So, for a short time, this one developer managed to mess with some huge companies and basically “broke the internet” by deleting just 11 lines of code.
That was only 11 lines of code, and it was seriously the most computationally expensive way to do “left-pad!”
So, it sounds like there’s more to this story. The way I understand it, it wasn’t the whole truth and that npm messed up. Kik didn’t actually have any claim to the “kik” package name, kind of like how Toyota wouldn’t have a right to a website address like example.com/toyota. Azer Koçulu isn’t the one in the wrong here; it’s actually Kik and the people at npm.
RE: Fact #22 (World of Warcraft’s Corrupted Blood Plague) – So, another time, something similar happened: A big raiding group managed to lure a really tough world raid boss from way out in the mountains all the way back to the main city in the game. This boss, Kazzak, had a timer where he’d become unbeatable, and of course, he was super angry by the time he got to Stormwind. It was a total disaster. Kazzak pretty much destroyed everyone in the city – players, the NPC guards, even the important characters who usually just give out quests.
Some brave folks kept respawning to try and defeat him, but most just watched as ghosts as Kazzak wiped everyone out. The game developers had to reset the whole server to get Kazzak back where he belonged, and then they created rules about how far players could follow things.
Kazzak also got healed every time he killed someone, which made him even tougher to beat.
RE: Fact #3 (Belgium Election Hit by Cosmic Ray) – He totally deserved to win. It was like even the universe was rooting for him!
RE: Fact #17 (F-16 Simulator Equator Sign Error) – So they were testing this out in the simulator, found a bug, and then fixed it.
RE: Fact #34 (Welchia Worm Tries to Patch Windows) – That’s a prime example of Chaotic-Good happening!
It’s pretty common for malware to patch up infected computers. Basically, the attackers don’t want anyone else getting access to the resources any more than the legitimate owner does. So, after they’ve taken control and set up their backdoors to stay in, it’s not unusual for the malware to then patch the system to prevent other vulnerabilities from being exploited.
This is a win-win for them in a couple of ways:
– They get to keep all the computer’s resources to themselves.
– The more malware there is on a system, the higher the chance it’ll be detected and removed.
I’d say this particular sequence of events is neutral evil.
Could someone explain the difference between malware, viruses, and worms in simple terms? Sorry to interrupt the thread.
Here’s a breakdown of what those terms mean, to clear things up:
**Virus:** Think of it like a biological virus, but for computers. It’s a bit of software that sneaks onto your computer, installs itself, and makes copies of itself to spread to other computers, all without you knowing. It usually latches onto other programs, files, or even the startup part of your hard drive.
**Malware:** This is just a shorthand for “malicious software.” It’s basically any software that’s designed to cause problems for your computer system, mess with your data, or make your computer do things you didn’t authorize.
**Trojan horse:** This is a sneaky type of malware. It looks like legit software, but hidden inside is malicious code. It creates hidden “back doors” into your system, often leading to data loss or theft.
**Worm:** Unlike a virus, a worm is its own thing – it doesn’t need to attach to anything. It just replicates and spreads to other computers, often by taking advantage of security weaknesses on a network.
**Spyware:** This software spies on you without your knowledge. It can keep tabs on what you’re doing on your computer, like recording what you type or stealing things like credit card details.
**Adware:** This is software that automatically pops up ads or banners to make money for its creator. Some free software uses adware, and it’s not always harmful. But if it gets too intrusive or sneaky, it can be considered spyware or malware.
RE: Fact #21 (Dan Saunders ATM Exploit Spree) – He quoted “It was super addictive being able to just type and see your account balance jump into the millions. I felt like a caveman who just discovered fire.”
I bet it was Dan. I bet it was.
Reminds me of when I used to find cheat codes or exploits in games. It’s awesome seeing everyone share cheat codes for games; it brings back so many great gaming memories.
Is that kind of partying as fun as people say?
The “money doesn’t buy happiness” folks seem to be pretty quiet lately.
I’m just glad this happened to someone who’d have fun with it, instead of someone like me who’d probably just use it to pay off debts or invest in market shares or something equally boring.
RE: Fact #48 (Michael Collins Fixes Apollo 11 with Switch) – Environmental Control System Malfunction
Procedure 17:
Turn the power off.
Turn the power on.
Check if the Environmental Control System is working normally.
Hey, I’m Clippy! Looks like you’re trying to restart the Environmental Control System. I can totally help you with that.
RE: Fact #20 (Nebraska Woman Exploits Gas Pump Glitch) – A few years back, I found a weird bug in a Coca-Cola machine. It only acted up when a drink was sold out and you paid with a card.
Basically, the machine would try to charge your card for two sodas, thinking you’d buy two. But if you only wanted one and finished the order, it would only charge for one, and you’d get your drink.
However, if you picked your first drink and then chose the sold-out item for your second, the machine would attempt to give you the sold-out item. After a couple of failed attempts, it would cancel the whole thing, leaving you with one free drink.
From what I could tell, I was the only one who figured this out. The machine eventually broke and was removed, but I’m not sure if they ever figured out what was wrong with it.
So, back when I was a teen and chilling at the Y, I totally stumbled upon this trick. If you put money in the drink machine and just held down the button, it would keep spitting out drinks! I basically lived like royalty that summer.
RE: Fact #20 (Nebraska Woman Exploits Gas Pump Glitch) – That’s a ton of gas! Sounds like someone’s definitely siphoning it off and selling it. They probably wouldn’t have even batted an eye if it was just for personal use.
Selling fuel is tougher than it seems. I remember seeing a documentary about it from some folks in Philadelphia.
Yeah, I work in oil.
I saw a documentary about something similar, but it was about some guys up in Canada. They were trying to disguise what they were doing by selling coupons for hair perms. The people looking into it actually thought it was related to prostitution, but it turned out they were just getting actual hair perms! I think it was set in a trailer park.
RE: Fact #2 (Cosmic Rays Flip Memory Bits) – So, if you’re thinking about opening a computer repair shop, Denver’s the place to be. Got it.
RE: Fact #3 (Belgium Election Hit by Cosmic Ray) – It’s called a single-event upset, or SEU for short. It can happen in things like processors or memory. Basically, when a particle hits, it creates a charge that can flip the state of a crucial part of the chip, causing a glitch. The result is an error in how the device works, and it’s often called a “soft error.”
RE: Fact #26 (Josh Muszynski’s $23 Quadrillion Charge) – If you’re curious why this happened, here’s the breakdown. The charge was supposed to be $46.88, probably for a carton of cigarettes. They removed the decimal but kept the cents, converted that to hex, and then replaced the first six hex bytes with spaces. When converted back to decimal, it ended up being $23,148,855,308,184,500.
Here’s something wild: each extra space you add makes the number jump up astronomically. For instance, if there were 13 spaces instead of 12, the charge would be $592,610,695,889,524,101,712 – that’s 592 quintillion dollars! It probably added 8 spaces instead of 7, resulting in a charge of $151,708,338,147,718,170,939,984 sextillion dollars. That’s roughly 2.5 billion times the combined GDP of all countries on Earth.
RE: Fact #16 (Deep Blue Bug Shakes Kasparov) – If the computer made a random move and still won, then yeah, I’d say Kasparov totally threw the match.
He didn’t just lose the match; he pretty much gave up and lost the whole thing. That move was so weird, it was like he thought the computer was a thousand moves ahead and had already won, so advanced he never stood a chance.
And yet, it’s still seen as the moment computers beat humans. But really, it was just human weakness and insecurity losing, not some super-smart computer.
Still a great story, though.
Sounds like computers won out because people weren’t strong enough or were too insecure.
You can watch the matches online. Kasperov was really arrogant and didn’t practice, thinking a computer couldn’t play creatively.
Kasperov actually won the first set of matches. Back then, Deep Blue was programmed to scan strategies and come up with counters. Kasperov totally dominated the machine, using well-known strategies and making quick changes on the fly to throw it off, which left Deep Blue vulnerable.
IBM really needed this win, as their stock price was on the line. In 1997, Kasperov was asked to play Deep Blue again, but he declined, feeling he had nothing to gain and was just being paid to play.
When he did play again, he won the first match easily. The IBM engineers quickly tweaked some of the code. In the second match, a famous glitch occurred. Kasperov suspected the IBM engineers were messing with the code and accused them of using a human player. He stormed out and forfeited.
Kasperov won the third match easily.
Deep Blue took the fourth match.
It all came down to the fifth game. Deep Blue made another odd move, and Kasperov resigned, leaving and claiming the whole thing was a fraud.
Sounds like Kasparov is being a jerk about this. I’m familiar with the situation, but I’m not super into chess.
RE: Fact #25 (John Kane Hacks Video Poker Bug) – Basically, a keyboard is just a bunch of buttons you can press, and the way you combine those presses is what lets you hack a computer.
There are laws against accessing systems without permission, not about the actual act of typing that allows for hacking. I can totally access my own server however I want since I’m authorized, so it’s not illegal for me to type those commands.
This is a public machine with a glitch in the public-facing software. It’s not really hacking, just like it wouldn’t be hacking if a website accidentally let you place an order for free because of a bug.
RE: Fact #4 (Jimmy Zhong Exploits Silk Road Bug) – Tough situation, getting a year in jail after swiping $3.4 billion. That’s rough.
He didn’t get to keep it. If he had, it would’ve been worth it.
He was still a billionaire for 10 years before he got caught.
RE: Fact #48 (Michael Collins Fixes Apollo 11 with Switch) – So, it looks like procedure 17 in the manual is pretty much just a more complicated way of doing a power cycle on the component.
RE: Fact #7 (GPS Timing Error Disrupts Networks) – Yeah, in IT, if a device gets out of sync with a domain controller on time, it can lose network access and even get “tombstoned.” Could something like that happen up there?
Just a heads-up, GPS started as a military thing, so you probably won’t find many details on its operational security easily.